DEVOURED
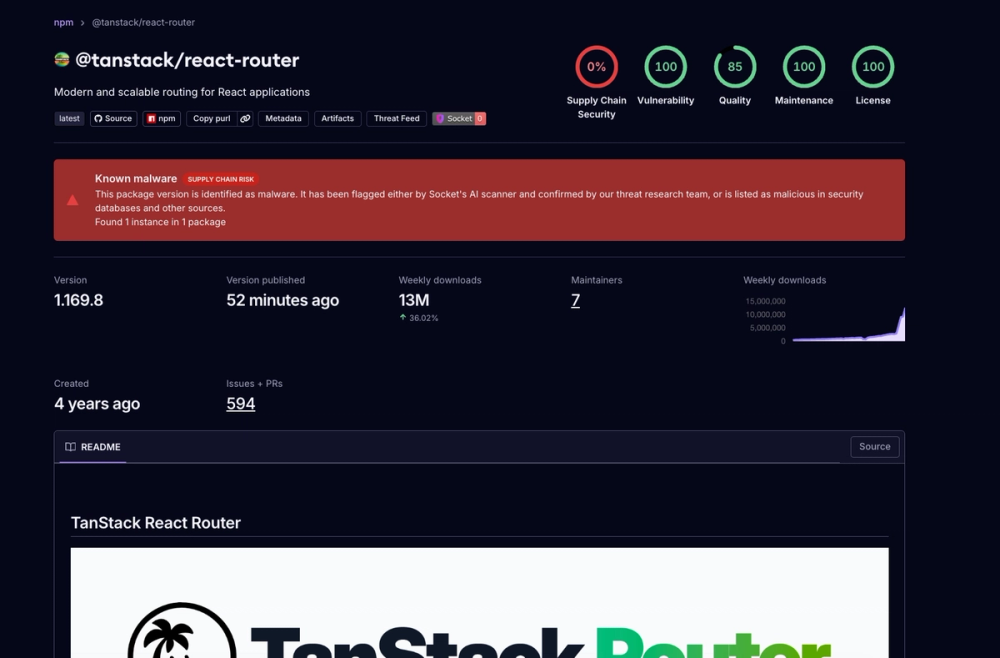
TanStack npm Packages Compromised in Ongoing Mini Shai-Hulud Supply-Chain Attack
84 TanStack npm packages with 12M+ weekly downloads were compromised in a supply-chain attack, forcing TanStack to deprecate affected versions and harden their GitHub Actions workflow.
What: Attackers compromised 84 TanStack npm packages including widely-used libraries with over 12 million weekly downloads. TanStack responded by deprecating affected versions, engaging npm security to remove malicious tarballs, purging GitHub Actions cache entries, and merging workflow hardening changes including repository-owner guards and pinned third-party action references.
Why it matters: This attack, dubbed Mini Shai-Hulud, demonstrates how GitHub Actions workflows remain a high-value target for supply-chain compromise. The scale of affected downloads shows how a single workflow vulnerability can cascade across the entire npm ecosystem.
Takeaway: If you use TanStack packages, check the Socket.dev article for the list of compromised versions and follow their recommended remediation actions for affected systems.
Decoder
- Supply-chain attack: Malicious code injected into legitimate software packages during the build or distribution process, compromising all downstream users who install the package.
- GitHub Actions cache: GitHub's workflow caching mechanism that can be exploited to persist malicious code across workflow runs if not properly secured with repository-owner guards.
Original article
GemStuffer Campaign Abuses RubyGems as Exfiltration Channel Targeting UK Local Government
GemStuffer abuses RubyGems as an exfiltration channel, packaging scraped UK council portal data into junk gems published from new accounts.
Explore all 40 articles in today's digest
Fresh dev news, AI-digested daily. Never miss a trend at devoured.fyi