DEVOURED
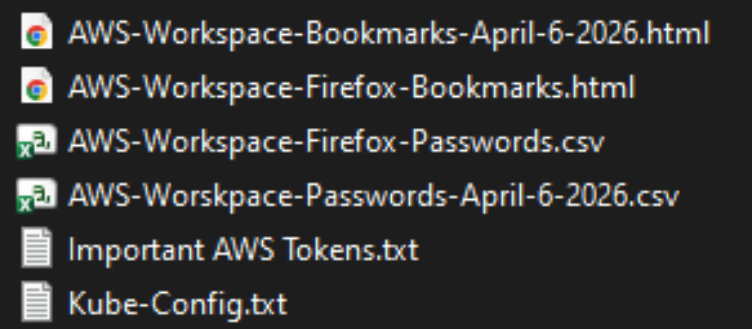
CISA Admin Leaked AWS GovCloud Keys on Github
A CISA contractor accidentally exposed highly privileged AWS GovCloud keys, internal system credentials, and plaintext passwords in a public GitHub repository, deemed one of the most egregious government data leaks recently.
What: A contractor for the Cybersecurity & Infrastructure Security Agency (CISA), working for Nightwing, created a public GitHub repository named "Private-CISA" which exposed administrative credentials for three AWS GovCloud servers, plaintext passwords for dozens of internal CISA systems (including "LZ-DSO" for DevSecOps), and CISA's internal "artifactory." Security researcher Guillaume Valadon of GitGuardian discovered the leak on May 15, 2026, and Philippe Caturegli of Seralys confirmed the validity of the AWS keys, which remained active for 48 hours after CISA was notified.
Why it matters: This incident starkly reveals the persistent challenge of human error in security, even within agencies dedicated to cybersecurity, underscoring the critical need for robust automated secrets scanning, strict organizational GitHub policies, least-privilege access, and short-lived credentials, especially when developers treat repositories as informal synchronization tools.
Takeaway: Developers should ensure secrets scanning is enabled for all repositories, never disable GitHub's secret detection features, and use temporary, least-privilege credentials for cloud access. Organizations need to enforce strict policies around public repositories and credential management.
Deep dive
- A contractor for CISA, working for the company Nightwing, exposed sensitive credentials and internal system details in a public GitHub repository named "Private-CISA."
- The leak included administrative AWS GovCloud keys for three accounts, plaintext usernames and passwords for dozens of internal CISA systems (like "LZ-DSO," their secure code development environment), and access to CISA's internal "artifactory" (code package repository).
- Guillaume Valadon, a researcher at GitGuardian, discovered the exposed secrets on May 15, 2026, and alerted KrebsOnSecurity after CISA was unresponsive.
- Philippe Caturegli, founder of Seralys, validated the AWS keys, confirming high-level access, and noted that the contractor had disabled GitHub's default secrets detection.
- Caturegli suggested the repository was likely used as a "working scratchpad or synchronization mechanism" between work and home computers, with commits dating back to November 2025.
- The exposed credentials included easily-guessed passwords, such as platform names followed by the current year.
- CISA stated there was "no indication that any sensitive data was compromised" but is investigating and implementing additional safeguards.
- The GitHub account was taken offline, but the exposed AWS keys remained valid for an additional 48 hours after CISA was notified.
- The article highlights CISA's reduced budget and staffing, having lost nearly a third of its workforce since the start of the second Trump administration.
Decoder
- AWS GovCloud: Isolated AWS regions designed to host sensitive data and regulated workloads, meeting U.S. government compliance requirements (e.g., FedRAMP High, DoD SRG).
- Secrets scanning: Automated tools or processes used to detect and prevent sensitive information (like API keys, passwords, or access tokens) from being committed to code repositories.
- Artifactory: A universal repository manager that supports all major package formats, providing a single source of truth for all packages, binaries, and dependencies.
- Least-privilege cloud access: A security principle where users, programs, or processes are granted only the minimum permissions necessary to perform their intended tasks.
- Short-lived credentials: Security credentials (like temporary access keys or tokens) that are valid for a very limited time, reducing the risk if they are exposed.
Original article
Full article content is not available for inline reading.
Explore all 51 articles in today's digest
Fresh dev news, AI-digested daily. Never miss a trend at devoured.fyi